Glass lattice cubes stacked on a tilted slab in cool light

The controls every
app ships with

Chamfer fits SSO, roles, sign-offs and an exportable Logbook to every app, whether it came from the Bench, Chamfer MCP or an imported repo. Builders keep their pace; security sees all of it.

Chamfer fits SSO, roles, sign-offs and an exportable Logbook to every app, whether it came from the Bench, Chamfer MCP or an imported repo. Builders keep their pace; security sees all of it.

01

One place for every AI-built app

Apps from the Bench, from Claude over Chamfer MCP, or imported from an old repo all land in one workspace, behind one sign-in.

02

Rules a prompt can’t remove

Tolerances run in Chamfer’s runtime, outside the generated code. A builder can change a layout by prompt. Nobody can prompt away a permission.

03

Reviews in a queue, not a meeting

Each release reaches security with its diff, its data sources and the roles it changes. A named approver signs it off, and the builder moves on.

01 — Tolerances
Four controls, fitted to every app from its first version

Four controls, fitted to every app from its first version

Four controls, fitted to every app from its first version

01

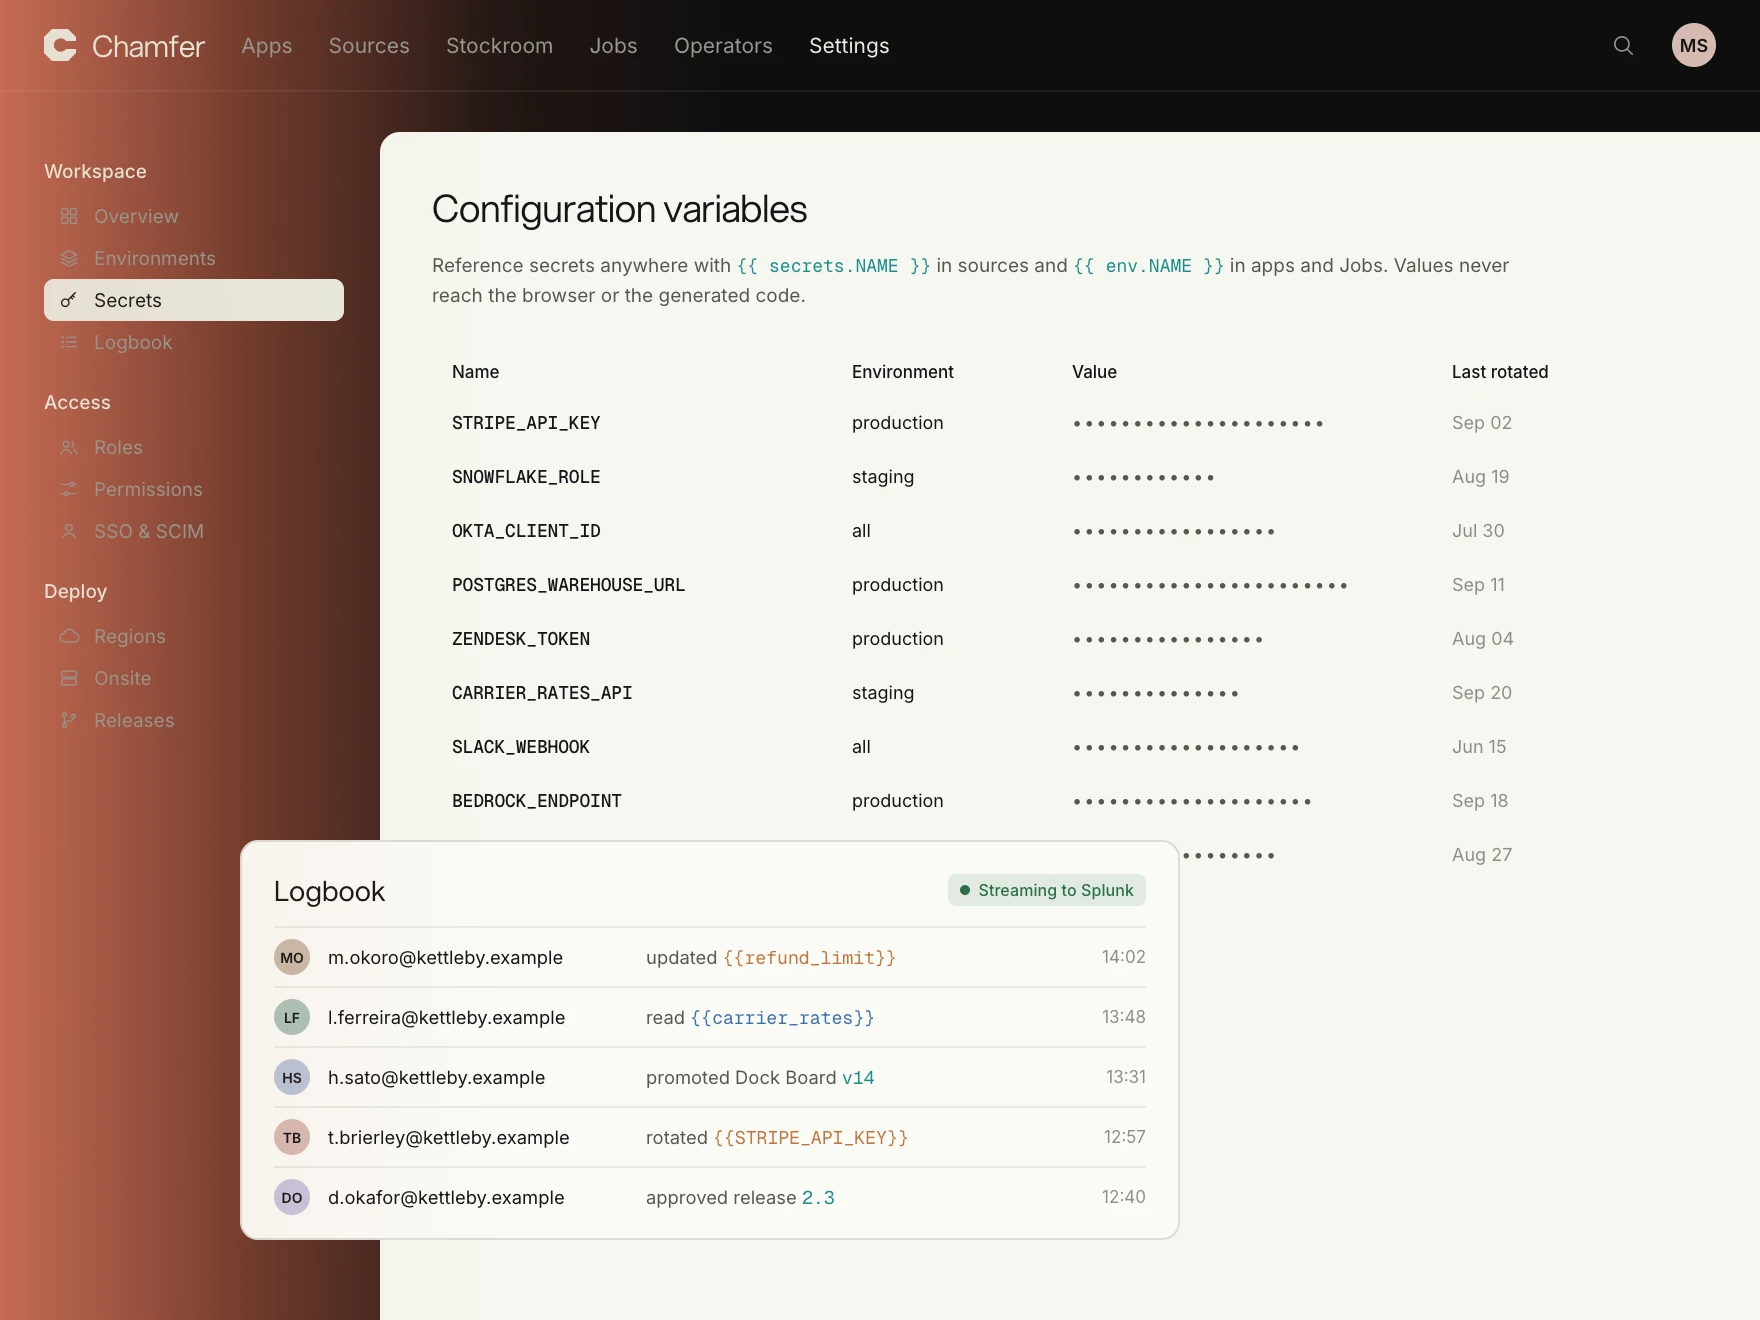
Secrets masked, every change logged

Credentials live in Chamfer’s secret store and never reach the browser or the generated code. Every read and edit is written to the Logbook.

02

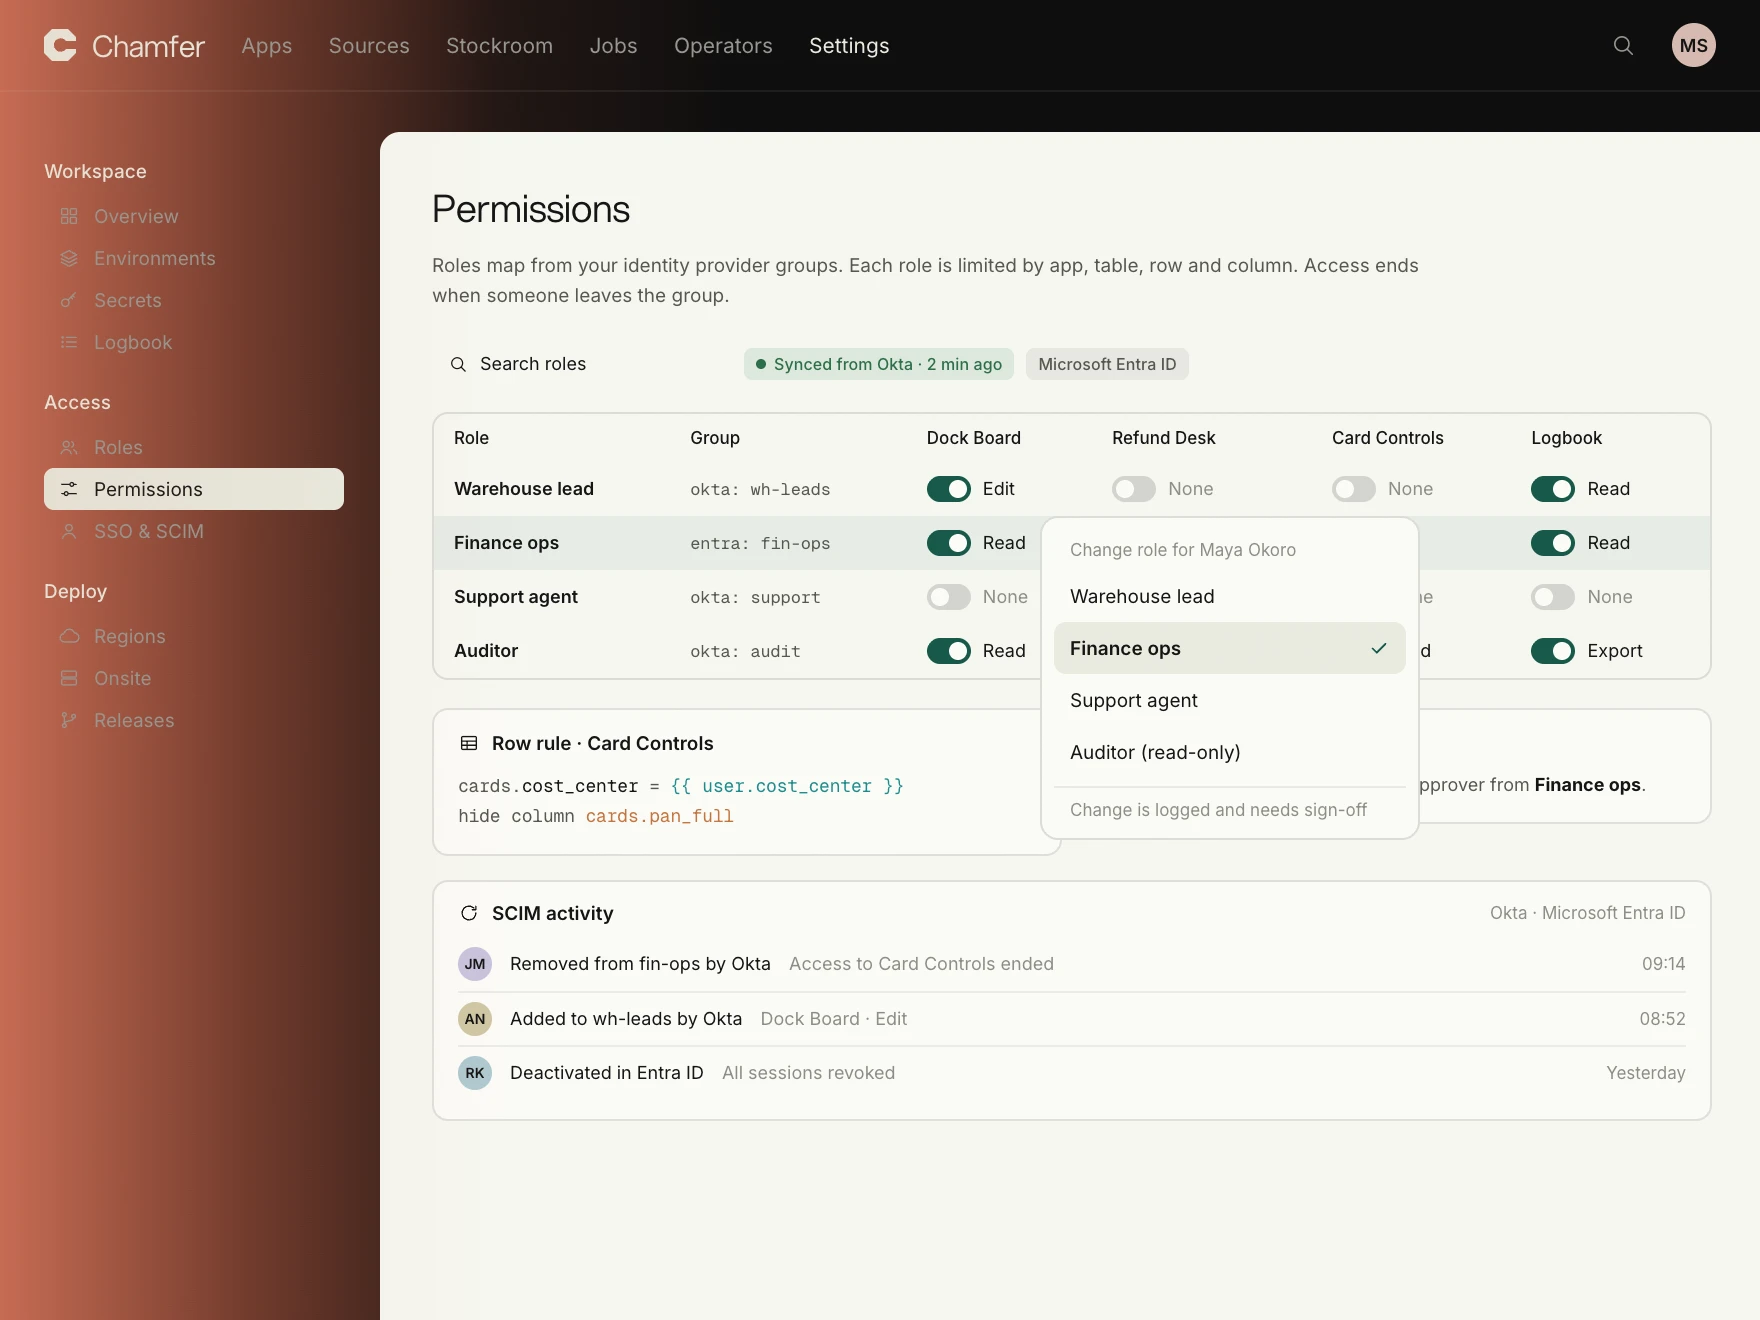
Access down to the row

Map roles from Okta or Microsoft Entra ID, then limit each one by app, table, row and column. Access ends when someone leaves your identity provider.

03

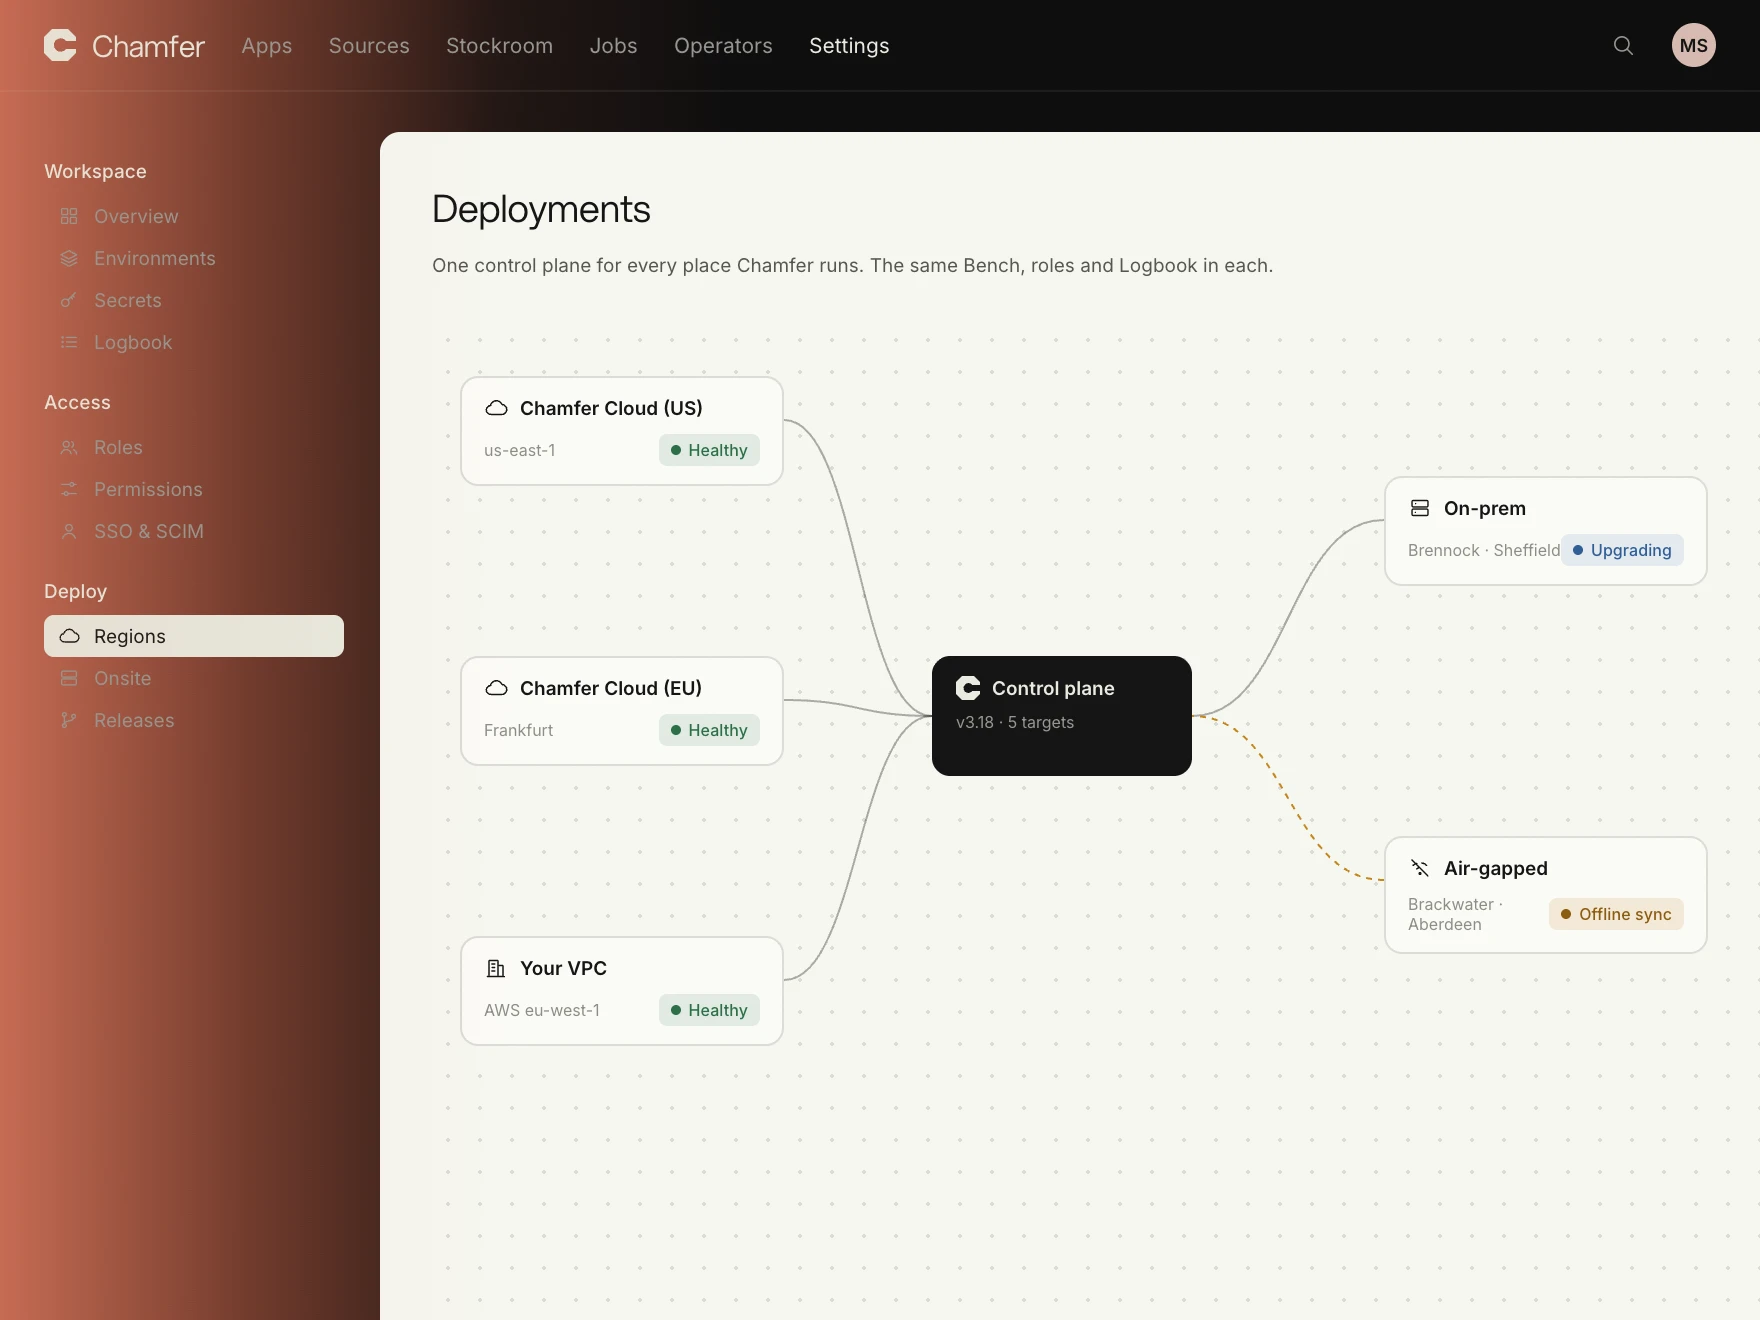
Run it where your data lives

Use our US or EU cloud, or run Chamfer Onsite in your VPC, on-prem or air-gapped. Same Bench, same controls, one console.

Chamfer console showing masked configuration variables and a Logbook of recent changes
Chamfer permissions matrix with roles mapped from Okta and a row rule
Chamfer deployments view with one control plane linked to cloud, VPC, on-prem and air-gapped targets

01

Secrets masked, every change logged

Credentials live in Chamfer’s secret store and never reach the browser or the generated code. Every read and edit is written to the Logbook.

02

Access down to the row

03

Run it where your data lives

Chamfer console showing masked configuration variables and a Logbook of recent changes
Chamfer permissions matrix with roles mapped from Okta and a row rule
Chamfer deployments view with one control plane linked to cloud, VPC, on-prem and air-gapped targets

02 — Controls

Six controls your reviewer will ask about

01

Sign-in through your identity provider

SAML 2.0 or OIDC with Okta, Microsoft Entra ID or Google Workspace. SCIM 2.0 creates, updates and removes users for you.

SAML 2.0

OIDC

SCIM 2.0

02

Roles down to the row and column

Group-mapped roles decide who opens, edits or approves each app. Row and column rules decide which records they see.

RBAC

Row-level

Column-level

03

A Logbook you can export

Every prompt, query, deploy and permission change, with a name, a timestamp and a diff. Stream it to your SIEM or export a CSV.

Splunk

Datadog

Amazon S3

CSV

04

Secrets kept server-side

Credentials sit in Chamfer’s store or your own, masked in the editor and never written into generated code.

AWS Secrets Manager

GCP Secret Manager

Doppler

05

Encrypted, and kept in region

AES-256 at rest and TLS 1.2+ in transit. Choose US or EU (Frankfurt) residency, or keep everything in your network with Onsite.

AES-256

TLS 1.2+

US

EU

06

A person releases AI writes

Operators and Jobs can draft a change to payments, payroll or patient records. A named approver decides whether it runs.

Sign-offs

Two-person rule

Specs

03 — Comparison

The part that comes after the prompt

Typical AI app builders

Chamfer

Single sign-on and roles on every app, prototypes included

Single sign-on and roles on every app, prototypes included

Credentials held server-side, never pasted into generated code

Credentials held server-side, never pasted into generated code

Every action kept in the Logbook for 400 days, longer on Enterprise

Every action kept in the Logbook for 400 days, longer on Enterprise

Writes to payments, payroll or patient data wait for a named approver

Writes to payments, payroll or patient data wait for a named approver

Run the whole platform in your own cloud with Chamfer Onsite

Run the whole platform in your own cloud with Chamfer Onsite

“We exported the answer from the Logbook before the meeting ended.”

Halden Mutual

212 apps certified for access in one afternoon

212 apps certified for access in one afternoon

  • Kettleby Freight logo
    Halden Mutual logo
    Tessaly logo
    Brackwater Energy logo
    Quenby logo
    Fennimore Health logo
    Saltmarsh & Co. logo
    Brennock Precision logo

Held to these controls at 1,400 companies, from clinics to card issuers

SOC 2 Type II
ISO 27001
GDPR DPA
HIPAA BAA

Compliance seals are placeholders. Replace them with the certifications your company holds, or remove them.

Inspection block detail

From first prompt to 400th app, one rulebook

From first prompt to 400th app, one rulebook

From first prompt to 400th app, one rulebook

04 — Questions

Questions from security teams

Where does Chamfer store our data?

Do you run penetration tests?

Can we self-host Chamfer?

Do model providers see or keep our data?

Which identity providers work with Chamfer?

Build it fast.
Keep the receipts.

See what each plan includes on the pricing page, or book a security walkthrough.

Create a free website with Framer, the website builder loved by startups, designers and agencies.